


The PHP security team published a critical advisory on Wednesday, 21 October, together with versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Two vulnerabilities, both CVSS v4.0 9.2, can allow unauthenticated remote code execution. This is an emergency patch, not a permanent global internet outage.
Tuesday’s notice scheduled the release for 14:00 UTC. php.net says the PHP runtime itself must be updated, not only themes or plugins. “There are no complete mitigations, updating is the only safe choice.” PHP 8.1 and older no longer receive updates from the project; LTS vendors may have backports. A vendor’s instruction, not an inventory of Romanian sites.
Cloudflare wrote that it had WAF rules in place from 21 October, 03:02 UTC, about nine hours before public disclosure, and that it saw attack traffic aimed at customers. Dane Knecht, quoted by News.ro, said the first attacks were appearing and that the protections were temporary. A WAF, not a substitute for the patch.
News.ro headlined that part of the world internet had been put offline. The facts in the body are narrower: France’s Interior Ministry, cited by Reuters/Le Figaro, said prefecture websites had been taken down temporarily as a precaution until a patch. News.ro adds similar steps in the Netherlands and Finland, without quoting those ministries. A preventive offline, not a planetary blackout.
CVE-2026-109618 and CVE-2026-109619 sit in the runtime, not in one CMS. WordPress, Drupal, Joomla or Magento are examples of stacks that use PHP. Anyone whose host manages PHP needs the update there. Cloudflare still asks for the patch, with the WAF left on as an extra layer.
Until an incident tally, the closed fact is the PHP advisory, the security versions and the precautionary takedown of some public sites. This is not a permanent global outage.
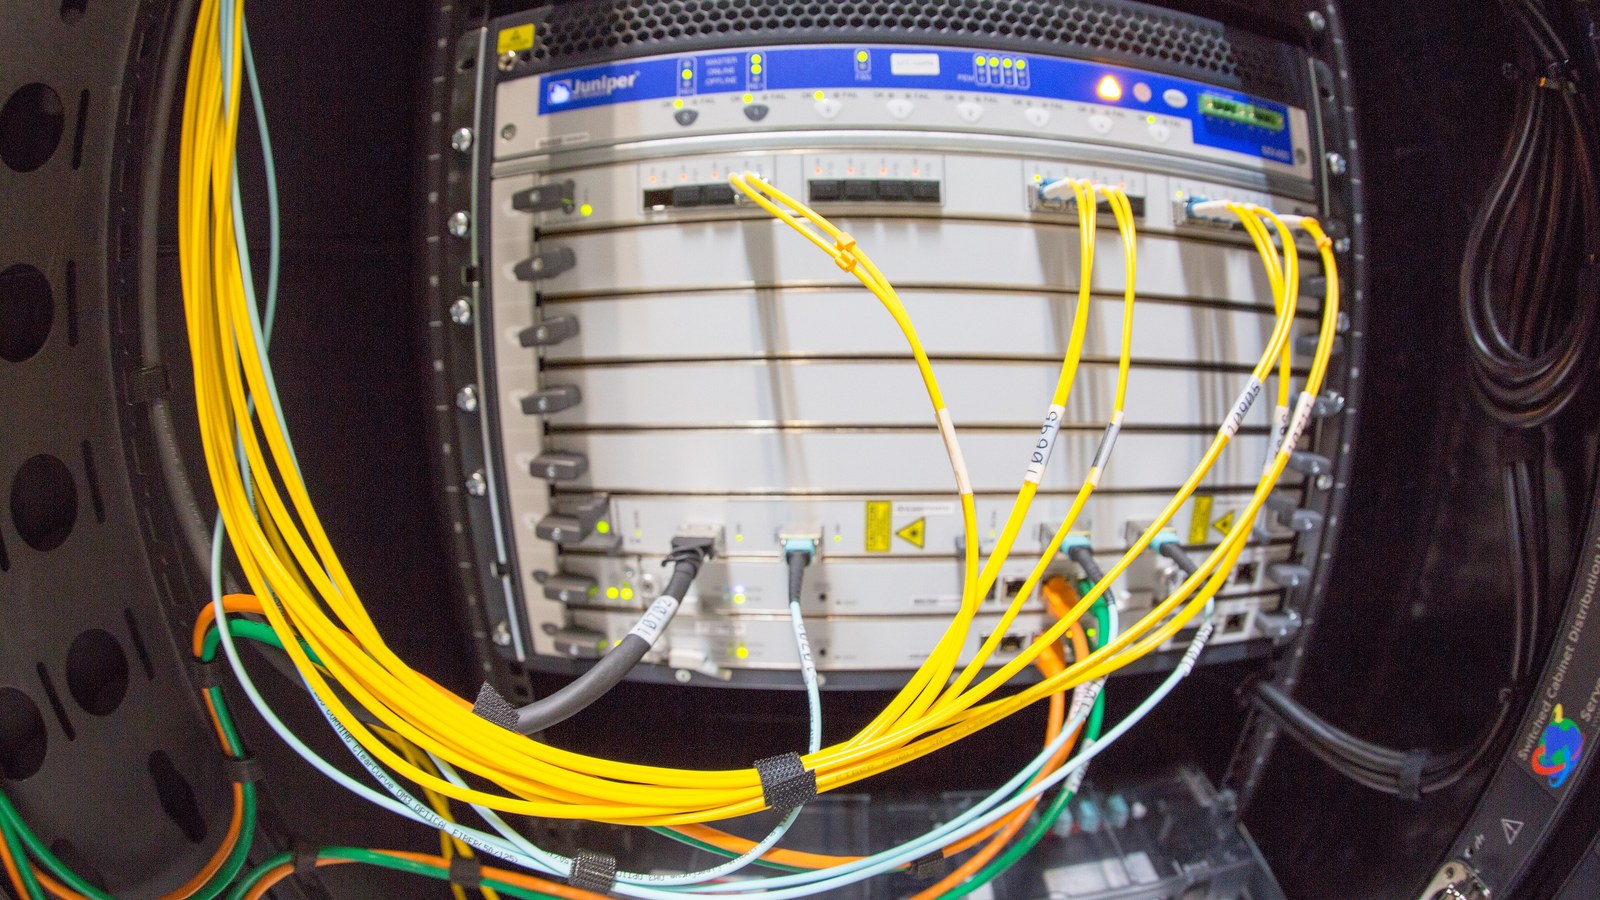
Image: VGrigas (WMF), Wikimedia Foundation servers, 21 July 2015, CC BY-SA 3.0, Wikimedia Commons; the 2015 room, not a photograph of the 21 October 2026 PHP patch.
Sources consulted: Part of the world internet put offline after two critical PHP vulnerabilities - News.ro; Security advisory: Critical remote code execution vulnerabilities, update now - PHP.net, 21 October 2026.
0 Comments
No comments on this article yet. Be the first!