


H2O Retailing and Hankyu Hanshin Department Store said on Monday, 19 October, that unauthorized access reached the customer system. Nearly all of about 1.26 million H2O ID members are in scope: some personal data leaked. That is not a confirmed card-dump figure. The company says it has not, so far, found misuse or secondary harm.
On Friday, 16 October, the access came through the Hankyu and Hanshin reservation site. They cut outside traffic and shut that site’s system. On Saturday, 17 October, the same kind of access hit HANKYU HANSHIN E-STORES and Remo Order; those went down too. On Monday, the inquiry showed the leak from the H2O ID base.
On the reservation path, the possible list, from the company’s notice: H2O ID, name (kanji and kana), gender, email, postcode, address, mobile, phone, age, date of birth and services used. Login passwords, the same note says, have not been confirmed as leaked.
E-STORES and Remo Order hold order history, some card data (type, last four digits, name, expiry) and some point-card data. The company does not keep the full card number or the security code. Whether those fields left or not is still an internal inquiry. We have not written that they left.
They told Japan’s personal-data commission and filed a police report. The services stay down until they say it is safe to restart. Members are getting emails. Sankei and Asahi repeat the same frame: nearly all members, not a handful of accounts.
The company asks people to watch messages that pretend to be it, by email or phone. Asahi gives two toll-free numbers, 10:00–20:00. This is an incident notice, not a conviction and not a final fraud tally.
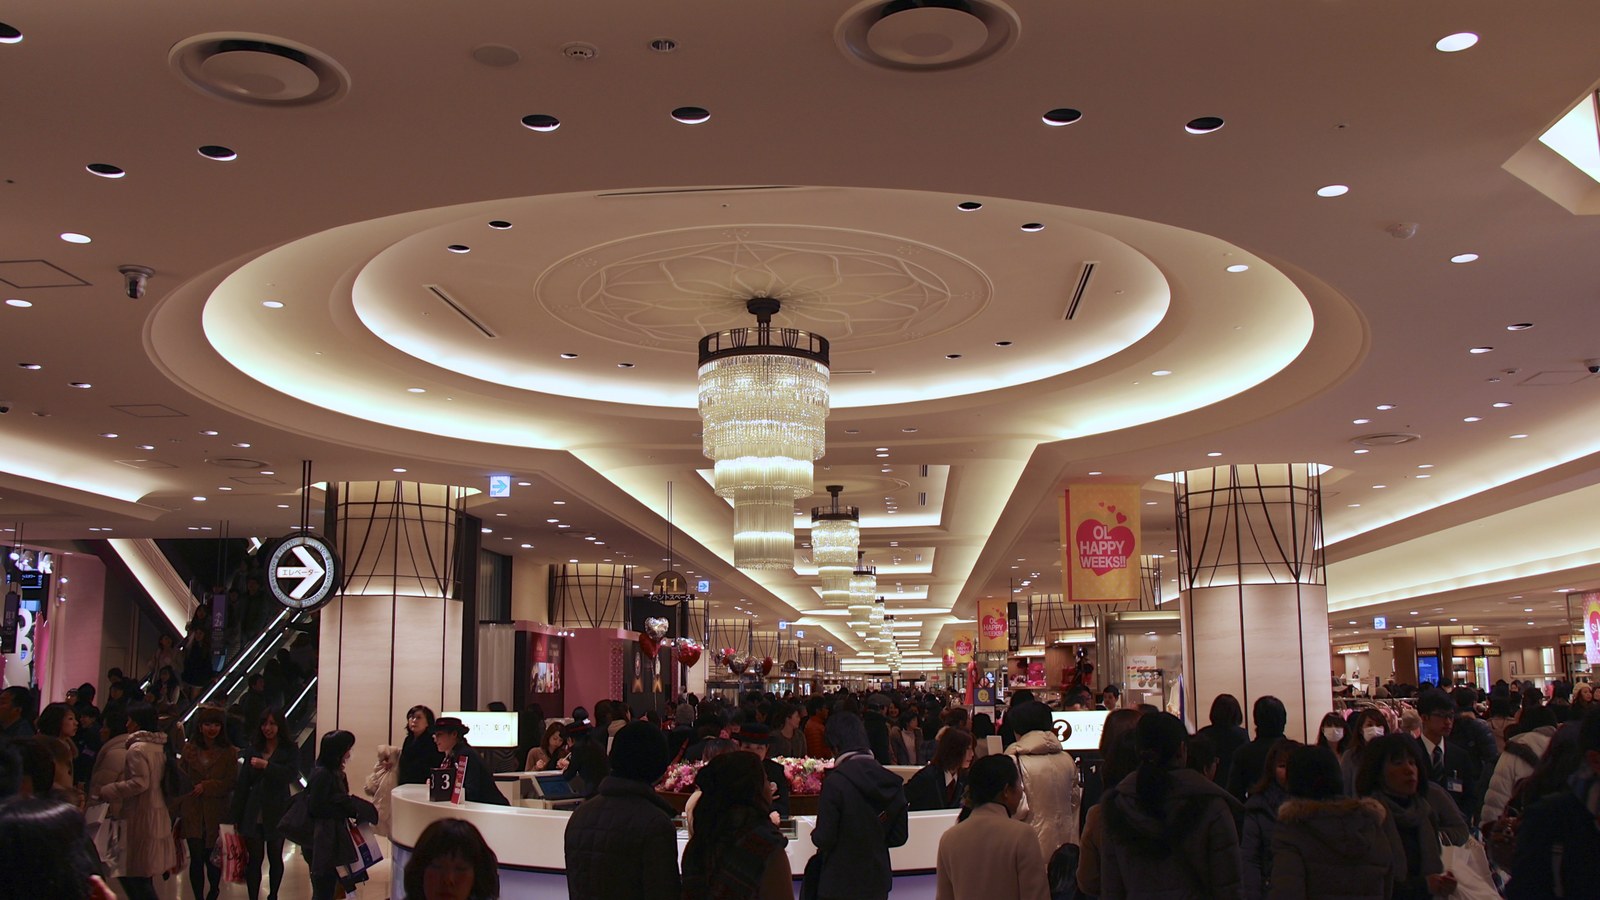
Image: Hankyu Umeda store, Osaka, 10 February 2013, Kanchi1979, CC BY-SA 4.0, Wikimedia Commons. Not a capture of the attack.
Sources consulted: Notice on unauthorized access and personal-data leak — Hankyu Hanshin Department Store; Hankyu Hanshin department stores also leak personal data, 1.26 million via reservation site — Sankei.
0 Comments
No comments on this article yet. Be the first!